 Every organization manages risk whether it realizes it or not. Decisions are made every day about employee safety, physical security, operations, business continuity, facility protection, and emergency preparedness. The difference between successful organizations and struggling organizations is rarely the absence of risk. It is the ability to identify risks before they become incidents.
A risk assessment provides the framework for making informed decisions about those threats. Whether the concern involves workplace safety, physical security, natural disasters, workplace violence, criminal activity, utility disruptions, or business continuity, a risk assessment helps organizations understand what could happen, how likely it is to occur, and what controls are necessary to reduce the impact.
Many organizations rely on standard policies and baseline security or safety controls. While minimum standards provide a strong starting point, no two facilities face identical risks. A manufacturing plant in a tornado-prone region faces different challenges than a distribution center in a high-crime urban area. A healthcare organization faces different threats than a warehouse or office building.
This is why risk assessment remains one of the most important tools in environmental health and safety, security management, and organizational resilience programs. As a risk management professional, Kevin Schmidt has extensive experience conducting site assessments, threat evaluations, security reviews, and operational risk analyses across diverse industries and facilities.
Why Risk Assessment Matters
Every workplace faces threats from both internal and external sources.
Without a structured evaluation process, organizations often allocate resources based on assumptions rather than actual exposure.
A comprehensive risk assessment helps organizations:
- Identify significant hazards and threats
- Prioritize resource allocation
- Support business continuity planning
- Strengthen safety and security programs
- Improve emergency preparedness
- Reduce operational disruptions
- Support regulatory compliance efforts
- Protect employees, assets, and reputation
Perhaps most importantly, risk assessments replace assumptions with data-driven decision-making.
What Is a Risk Assessment?
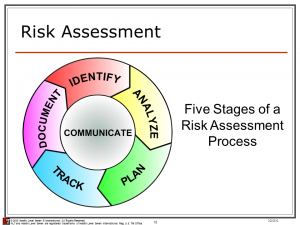
A risk assessment is a structured process used to identify threats, vulnerabilities, exposures, and business impacts associated with a facility, process, operation, or organization.
The goal is not simply to identify what could go wrong.
The goal is to understand:
- What threats exist
- How vulnerable the organization is
- How likely the event is to occur
- What consequences could result
- What controls already exist
- What additional controls may be needed
A quality risk assessment examines both probability and impact rather than focusing on either factor alone.
The Major Components of a Risk Assessment
Effective risk assessments evaluate multiple categories of risk because business operations rarely face a single threat source.
Environmental Factors
Environmental risks originate from natural or environmental conditions.
Common examples include:
- Tornadoes
- Hurricanes
- Flooding
- Earthquakes
- Wildfires
- Severe winter weather
- Extreme heat
- Chemical releases
- Utility failures
Organizations located in areas with recurring environmental threats often require controls beyond standard operating procedures.
Business Factors
Some facilities are inherently more critical than others.
Business-related risk factors may include:
- Revenue generation
- Proprietary information
- Intellectual property
- Critical manufacturing processes
- Distribution operations
- Customer-facing services
- Essential business functions
- Unique capabilities that cannot be duplicated elsewhere
The greater the business impact of an interruption, the greater the need for preventive controls and recovery planning.
Site Location and Facility Design
Physical characteristics significantly influence risk exposure.
Areas commonly evaluated include:
- Facility layout
- Access control measures
- Public accessibility
- Perimeter protection
- Lighting
- Surveillance coverage
- Fire protection systems
- Available emergency exits
- Building construction
- Natural barriers and terrain
A facility’s design often determines how effectively it can prevent, detect, delay, or respond to threats.
Municipal Resources
Organizations often rely on resources beyond their own property line.
Risk assessments should evaluate:
- Police response capabilities
- Fire department resources
- Emergency medical services
- Utility reliability
- Disaster response capabilities
- Mutual aid agreements
- Emergency management resources
A location with limited public resources may require additional internal preparedness measures.
Crime and Community Factors
External crime conditions frequently influence facility risk profiles.
Assessment considerations may include:
- Local crime rates
- Property crime trends
- Violent crime trends
- Organized criminal activity
- Civil unrest concerns
- Population density
- Economic conditions
- Neighborhood characteristics
Understanding local conditions allows organizations to align security controls with actual exposure levels.
Types of Risks Organizations Should Evaluate
A comprehensive risk assessment generally evaluates three major categories.
Natural Hazards
Natural hazards include events largely outside organizational control.
Examples include:
- Severe weather
- Tornadoes
- Flooding
- Earthquakes
- Wildfires
- Pandemics
- Utility disruptions
While these events cannot usually be prevented, their impact can often be reduced through planning and mitigation.
Human-Caused Incidents
Human-caused threats may originate internally or externally.
Examples include:
- Workplace violence
- Theft
- Vandalism
- Cyber incidents
- Sabotage
- Terrorism
- Civil disturbances
- Insider threats
These threats often require a combination of physical security, training, policies, and emergency planning.
Operational Risks
Operational risks develop from normal business activities.
Examples include:
- Equipment failures
- Supply chain disruptions
- Process breakdowns
- Staffing shortages
- Transportation interruptions
- Vendor failures
- Maintenance deficiencies
These risks are often overlooked despite having significant impacts on productivity and profitability.
How Risk Assessment Supports Physical Security
Many organizations begin with baseline security requirements.
These often include:
- Access control procedures
- Visitor management
- Security lighting
- Camera systems
- Locking hardware
- Alarm systems
- Employee identification procedures
However, baseline controls may not adequately address all locations.
A physical security risk assessment helps determine whether additional measures are necessary, such as:
- Enhanced access controls
- Security officers
- Vehicle barriers
- Panic alarms
- Ballistic protection
- Security screening
- Emergency notification systems
Effective security programs are built on identified risks rather than assumptions.
Understanding Risk Levels
Organizations often classify risk into categories to support decision-making and resource prioritization.
A common model includes four risk levels.
Extreme Risk
Extreme-risk locations face conditions that could create severe threats to employees, operations, or assets.
Examples may include:
- Active conflict zones
- Areas experiencing civil war
- Significant government instability
- Uncontrollable environmental threats
- Severe business disruption exposure
These situations often require extensive mitigation measures and executive-level oversight.
High Risk
High-risk locations experience elevated threats that require enhanced controls.
Potential factors include:
- Significant criminal activity
- Terrorism concerns
- Serious civil unrest
- Repeated security incidents
- Frequent environmental events
Additional protective measures are generally necessary to reduce exposure.
Moderate Risk
Moderate-risk locations face identifiable threats that can usually be managed through enhanced planning and controls.
Examples include:
- Elevated crime levels
- Emerging security concerns
- Regional disaster exposure
- Increased workplace violence risks
- Industry-specific threat conditions
These facilities often benefit from targeted improvements and periodic reassessment.
Low Risk
Low-risk locations generally experience limited exposure and can often operate safely using standard controls.
However, low risk does not mean no risk.
Every facility requires ongoing monitoring and periodic reassessment.
Common Mistakes During Risk Assessments
Many organizations unintentionally reduce the effectiveness of their risk assessment process.
Common mistakes include:
Focusing Only on Recent Incidents
Past events provide useful information, but emerging risks deserve equal attention.
Ignoring Employee Input
Employees often recognize developing hazards and security concerns before management does.
Treating Assessments as a One-Time Exercise
Risks evolve as facilities, communities, operations, and workforces change.
Evaluating Threats Without Evaluating Vulnerabilities
A threat creates risk only when a vulnerability exists.
Failing to Reassess
Mergers, facility expansions, staffing changes, and new operations can significantly alter risk profiles.
How Often Should Risk Assessments Be Conducted?
Organizations should establish a review schedule based on operational complexity and risk exposure.
Additional assessments should be conducted following:
- Significant incidents
- Facility expansions
- Business acquisitions
- New operational processes
- Major security events
- Natural disasters
- Regulatory changes
- Significant workforce changes
The objective is ensuring risk assessments remain current and relevant.
Risk Assessment and Business Continuity
Risk assessments serve as the foundation for effective business continuity planning.
Organizations cannot prepare for disruptions they have never evaluated.
Assessment findings often shape:
- Emergency response plans
- Crisis management programs
- Business continuity strategies
- Disaster recovery plans
- Physical security improvements
- Workplace violence prevention efforts
Without an understanding of risk, planning becomes guesswork.
Making Risk Assessment Part of Organizational Culture
The strongest organizations view risk assessment as an ongoing process rather than a compliance exercise.
Successful organizations:
- Conduct periodic reviews
- Track emerging threats
- Encourage employee reporting
- Analyze incident trends
- Update mitigation strategies
- Review changes in business operations
- Measure control effectiveness
Risk management works best when it becomes part of everyday decision-making.
The Bottom Line
A risk assessment helps organizations move from reacting to incidents to preventing them. By evaluating environmental hazards, business factors, facility vulnerabilities, community concerns, operational dependencies, and security threats, organizations gain a clearer understanding of where they are most exposed and what controls are needed to reduce risk.
No facility operates in a static environment. Crime trends change. Workforces grow. Operations expand. New threats emerge. Regular risk assessments provide the information leaders need to protect employees, maintain operations, allocate resources effectively, and build long-term organizational resilience.
If your organization has not conducted a comprehensive risk assessment recently, there is a good chance that your current risk profile no longer reflects today’s realities. The best time to identify critical vulnerabilities is before an incident forces you to discover them.